
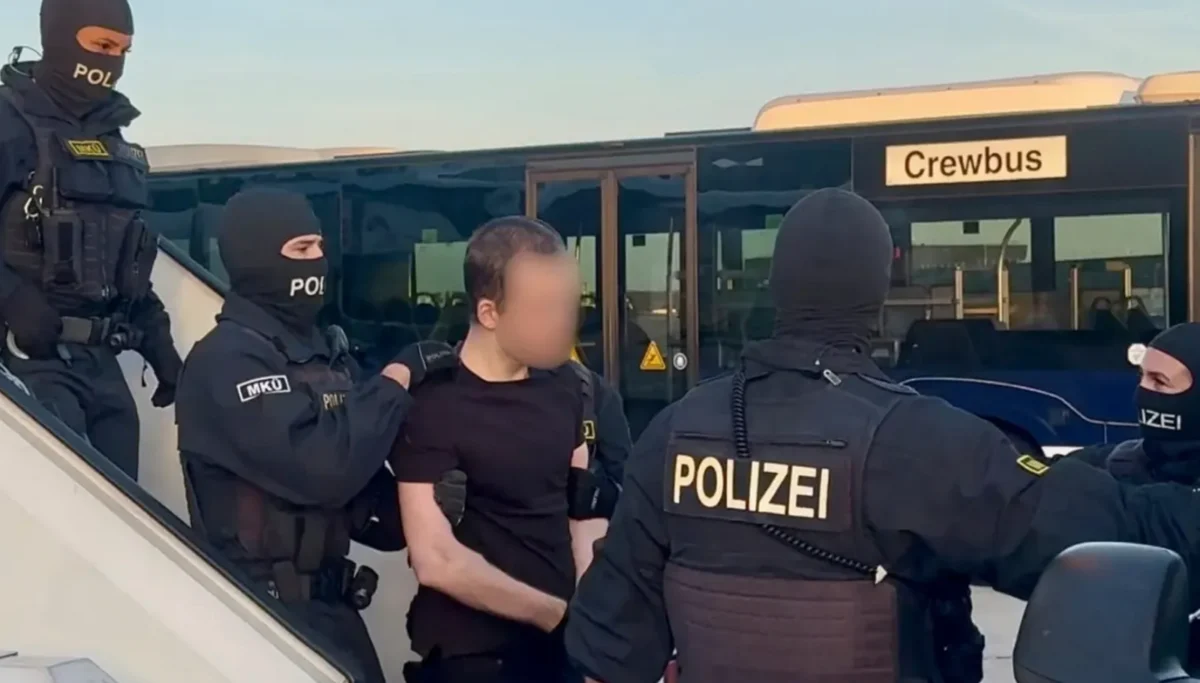
"The arrest of a suspected Qilin ransomware gang member in Japan marks a pivotal moment in global cybercrime enforcement, directly connecting a digital attack to a patient’s death within the UK’s National Health Service and potentially setting a groundbreaking precedent for ‘unlawful killing’ investigations in the cyber realm."
German authorities have successfully detained a Russian national, Vladimir K., accused of being a core member of the notorious Qilin cyber-crime gang. This significant international law enforcement operation has brought into sharp focus the severe real-world consequences of ransomware attacks, particularly after German detectives confirmed their investigation now includes the devastating 2024 hack on Synnovis, a pathology service critical to several London hospitals. This particular incident is unique, as it represents the first cyber-attack in history to be directly linked to a patient’s death, prompting British police to explore an unprecedented "unlawful killing" case.
The 28-year-old Russian suspect, Vladimir K., was apprehended in Japan in May while on a holiday trip. His travel plans were reportedly intercepted by intelligence agencies, leading to his arrest by Japanese police upon his entry into the country. He has since been extradited to Germany, where he was initially wanted for a September 2024 attack on a logistics company. In that incident, Qilin allegedly encrypted the company’s data and extorted approximately $160,000 in cryptocurrency. The broader investigation into Vladimir K. and his associates now encompasses their alleged involvement in the Synnovis breach, elevating the case to one of profound international and legal significance.
The Pervasive Threat of Qilin Ransomware

The Qilin cyber-crime gang has emerged as a formidable force in the global landscape of digital extortion since its tracking began in 2022. Operating a sophisticated ransomware-as-a-service (RaaS) model, Qilin is believed to have targeted over 4,000 organizations worldwide, extorting an estimated $140 million (£105 million) from its victims. Their modus operandi typically involves gaining unauthorized access to a victim’s network, encrypting critical data to render systems inoperable, and then demanding a ransom—often in cryptocurrency—for decryption keys. Many Qilin attacks also involve "double extortion," where sensitive data is exfiltrated before encryption, with the threat of public release if the ransom is not paid. This dual pressure tactic significantly increases the incentive for victims to comply.
The gang’s extensive victim list includes a diverse array of sectors, from educational institutions and local government bodies to major corporations and, most disturbingly, healthcare providers. Their disruptive capabilities were notably demonstrated in the high-profile October 2025 hack on Japanese beer maker Asahi, which caused significant operational delays and financial losses. The arrest of Vladimir K. in a non-traditional cybercrime hotspot like Japan underscores the growing reach and collaborative efforts of international law enforcement agencies determined to dismantle these transnational criminal networks. Historically, arrests of suspected Russian cybercriminals have been rare due to the Russian government’s general refusal to cooperate with Western law enforcement requests, making this extradition a particularly notable development.
The Synnovis Attack: A Turning Point for Cyber-Ethics
The attack on Synnovis, a diagnostics and pathology service operating as a crucial partnership between NHS trusts in London and the German company Synlab, occurred on 3 June 2024. The impact was immediate and catastrophic. A critical incident was declared across several major London hospitals, including King’s College Hospital NHS Foundation Trust and Guy’s and St Thomas’ NHS Foundation Trust. Pathology services, particularly blood testing and analysis, were severely disrupted, leading to a cascade of negative consequences for patient care.
Thousands of appointments were cancelled or delayed, non-urgent operations were postponed, and emergency patients had to be diverted to other hospitals, straining an already overburdened healthcare system. The ability to perform essential diagnostic tests, crucial for everything from routine check-ups to life-saving emergency care, was severely compromised. Doctors and nurses faced immense challenges in making timely and accurate diagnoses without access to critical blood test results, forcing them to rely on less efficient manual processes or make difficult decisions with incomplete information. The disruption persisted for weeks, highlighting the profound vulnerability of modern healthcare infrastructure to cyber threats.

However, the Synnovis incident transcended typical ransomware attacks with a chilling and unprecedented outcome: a patient’s death. A year after the hack, King’s College Hospital NHS Foundation Trust confirmed that one patient had "died unexpectedly," with a long wait for a blood test result identified as a significant contributing factor among several others. This revelation sent shockwaves through the cybersecurity and healthcare communities, directly linking a digital act of extortion to a tragic loss of life.
The "Unlawful Killing" Investigation: Setting a Precedent
The announcement that British police are examining whether the Synnovis inquiry could lead to an "unlawful killing" case represents a groundbreaking legal development. An unlawful killing verdict, typically associated with gross negligence manslaughter or corporate manslaughter, implies that a death was caused by the illegal act or omission of another party. Applying this legal framework to a cyber-attack is unprecedented and poses significant challenges.
For such a case to proceed, investigators would need to establish a direct causal link between the cyber-attack, the disruption of medical services, and the patient’s death. They would also need to demonstrate a level of criminal culpability on the part of the hackers, proving that their actions were not merely disruptive but directly contributed to the fatal outcome. This requires meticulous forensic analysis of digital evidence, detailed medical investigations, and a novel interpretation of existing legal statutes. Success in such a prosecution would set a powerful global precedent, potentially transforming how cyber-attacks on critical infrastructure are viewed and prosecuted, moving them beyond mere property damage or data theft to crimes against humanity.
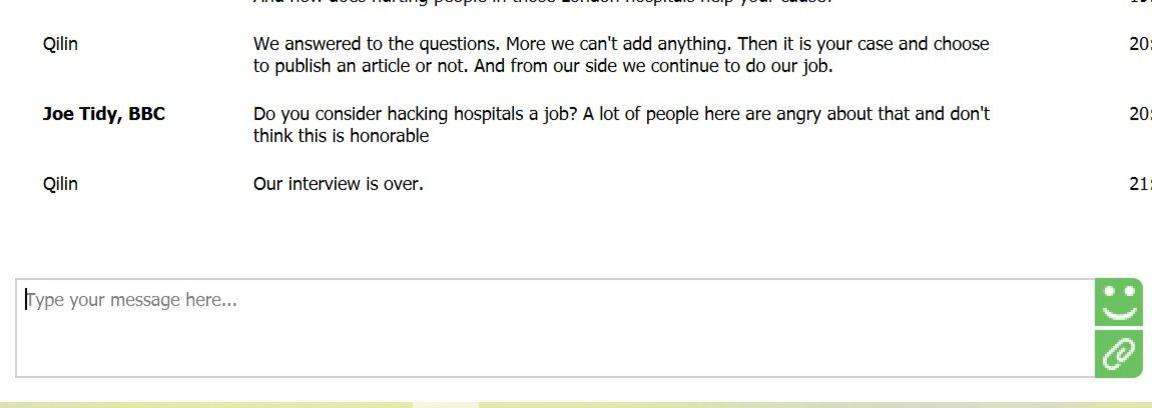
The hackers, after Synnovis refused to pay the ransom, eventually published the highly private patient data on their dark net website, further compounding the harm to victims whose sensitive medical information was exposed. At the time of the data leak, the Qilin group attempted to justify their actions to the BBC, claiming the hack was not solely for financial gain but also a protest against the UK’s perceived lack of support for Ukraine in its conflict with Russia. However, these claims were widely dismissed by experts as a thinly veiled attempt to politicize their criminal enterprise and distance themselves from the purely extortionist tactics for which Qilin is known.
Protecting Critical Infrastructure in a Digitally Interconnected World
The Synnovis attack serves as a stark reminder of the escalating risks posed by cyber-crime to critical national infrastructure, particularly healthcare. Hospitals, clinics, and diagnostic services are increasingly reliant on interconnected digital systems for everything from patient records and imaging to laboratory results and life-support equipment. This digital transformation, while offering immense benefits in efficiency and quality of care, also introduces profound vulnerabilities that malicious actors are eager to exploit.
The implications of such attacks extend far beyond financial loss. They can severely impair public health, erode trust in vital institutions, and, as tragically demonstrated by the Synnovis case, directly threaten human lives. Governments and organizations worldwide are grappling with how to adequately protect these essential services. This includes investing in robust cybersecurity defenses, implementing proactive threat intelligence, fostering international cooperation for intelligence sharing and law enforcement, and developing comprehensive incident response plans.
The arrest of Vladimir K. signifies a crucial step in the ongoing global effort to hold cybercriminals accountable. It sends a clear message that geographical boundaries offer diminishing protection for those who inflict harm through digital means. However, the unique challenges of attribution, jurisdiction, and the often state-backed nature of some cyber-crime groups mean that the fight against these sophisticated threats remains a complex and evolving battleground. The potential "unlawful killing" investigation stemming from the Synnovis hack could mark a new era in cyber-justice, forcing a re-evaluation of the legal and ethical responsibilities of those who wield digital weapons.
